This product was not featured by Product Hunt yet. It will not be visible on their landing page and won't be ranked (cannot win product of the day regardless of upvotes).
Product upvotes vs the next 3
Waiting for data. Loading
Product comments vs the next 3
Waiting for data. Loading
Product upvote speed vs the next 3
Waiting for data. Loading
Product upvotes and comments
Waiting for data. Loading
Product vs the next 3
Loading
DepSentinel
Block malicious dependencies before they reach your machine
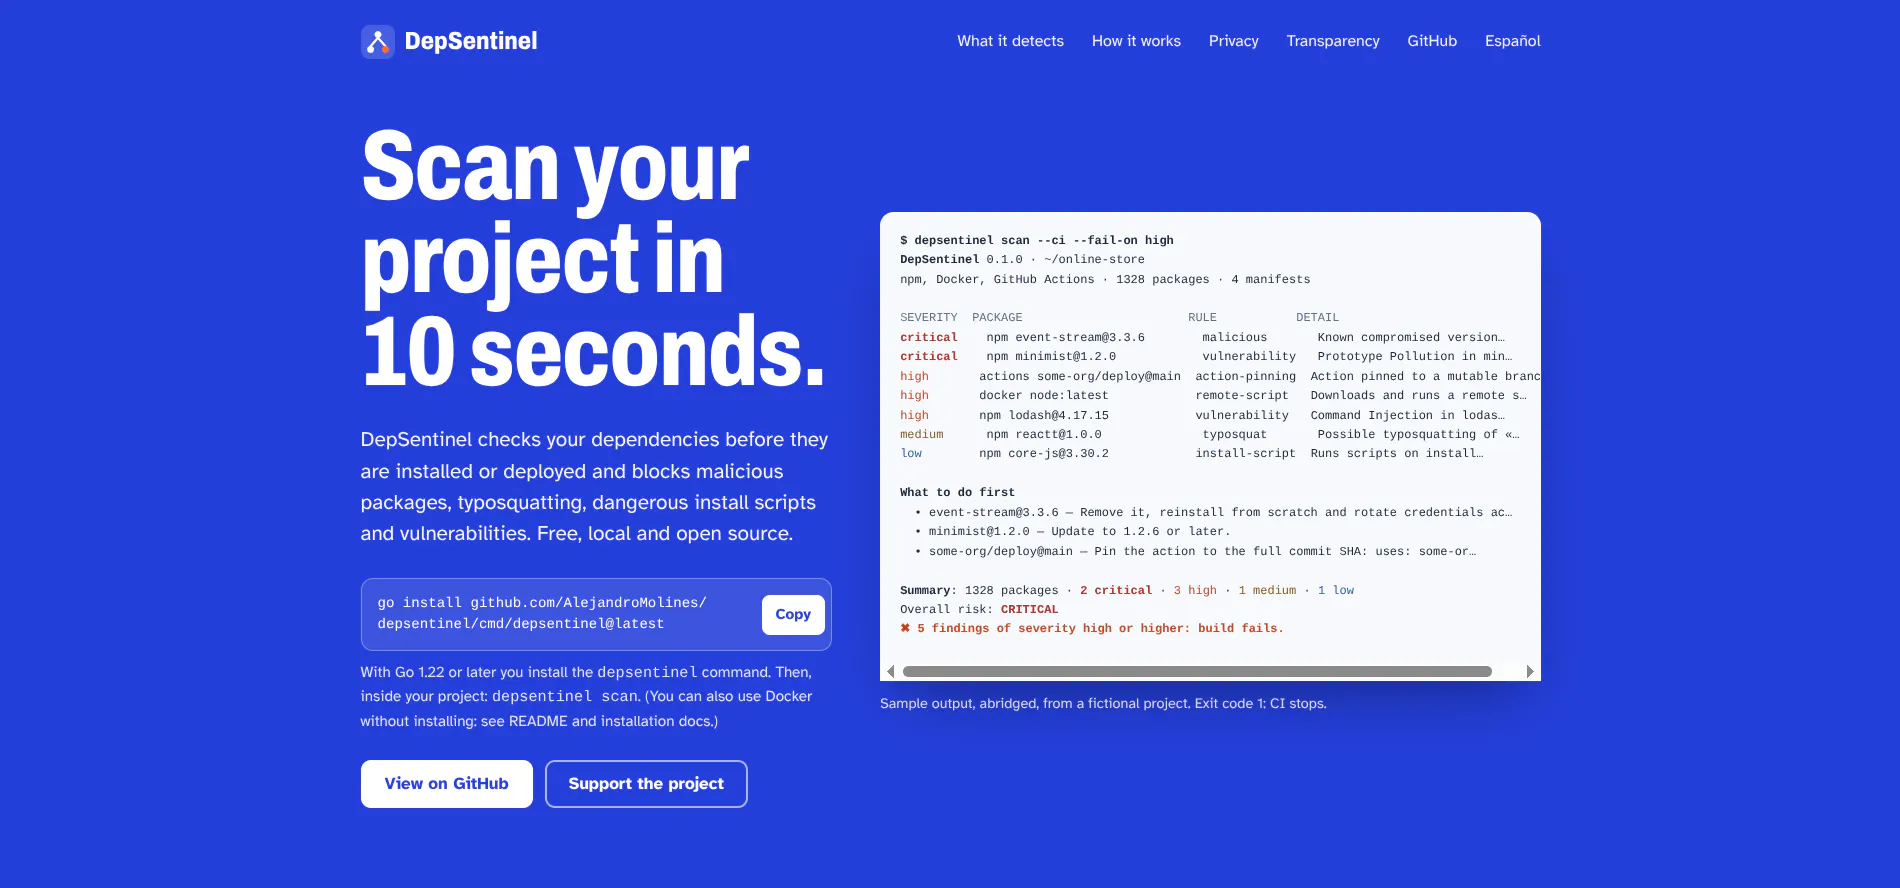
Blocks malicious packages, typosquatting and vulnerable dependencies before they reach your machine or production. Scans npm, PyPI, Go, Docker and GitHub Actions in seconds, 100% local, no account, no telemetry. Free and open source (MIT). Runs in CI and comments on pull requests. Includes a preventive guard: `depsentinel guard npm install` generates the lockfile with --ignore-scripts, scans it, and only then installs.
Hi Product Hunt! 👋
I built DepSentinel after a routine `npm install` pulled in over a thousand packages I had never read. Most of them transitive, some with install scripts, none reviewed. Supply-chain attacks (event-stream, ua-parser-js, colors.js…) keep happening and `npm audit` runs after the damage is already installed.
DepSentinel scans your lockfiles before anything runs: malicious packages, typosquats, suspicious install scripts, known CVEs, unpinned GitHub Actions and unpinned Docker images. It runs fully on your machine, no account, no telemetry, no server of ours.
The feature I'm most proud of is `depsentinel guard npm install`: it generates the lockfile with --ignore-scripts (so no install script runs), scans it, and only then runs the real install. That closes the window where a normal `npm install` already executed attacker code.
It's free, MIT-licensed and works in CI with a single `--ci --fail-on high`. Would love your feedback, especially false positives — there's a template for that.
Thanks for checking it out! 🛡️
About DepSentinel on Product Hunt
“Block malicious dependencies before they reach your machine”
DepSentinel was submitted on Product Hunt and earned 3 upvotes and 1 comments, placing #95 on the daily leaderboard. Blocks malicious packages, typosquatting and vulnerable dependencies before they reach your machine or production. Scans npm, PyPI, Go, Docker and GitHub Actions in seconds, 100% local, no account, no telemetry. Free and open source (MIT). Runs in CI and comments on pull requests. Includes a preventive guard: `depsentinel guard npm install` generates the lockfile with --ignore-scripts, scans it, and only then installs.
On the analytics side, DepSentinel competes within Open Source, Developer Tools, GitHub and Security — topics that collectively have 635k followers on Product Hunt. The dashboard above tracks how DepSentinel performed against the three products that launched closest to it on the same day.
Who hunted DepSentinel?
DepSentinel was hunted by AlejandroMolines. A “hunter” on Product Hunt is the community member who submits a product to the platform — uploading the images, the link, and tagging the makers behind it. Hunters typically write the first comment explaining why a product is worth attention, and their followers are notified the moment they post. Around 79% of featured launches on Product Hunt are self-hunted by their makers, but a well-known hunter still acts as a signal of quality to the rest of the community. See the full all-time top hunters leaderboard to discover who is shaping the Product Hunt ecosystem.
For a complete overview of DepSentinel including community comment highlights and product details, visit the product overview.

 AlejandroMolines